Tag: Fraud Management

  • ¿Cómo luchan los gestores de fraude en la industria de las telecomunicaciones a los estafadores?

    ¿Cómo luchan los gestores de fraude en la industria de las telecomunicaciones a los estafadores?

    Actualmente enfrentamos un brote global de COVID-19 con el consiguiente bloqueo, pánico y miedo en todo el mundo. Hemos seguido con atención los medios de comunicación para mantenernos actualizados sobre la situación. Si bien, de manera muy alentadora, más del 95% de la fuerza laboral ha comenzado a trabajar desde casa con una posible conectividad segura, los estafadores también han estado igualmente activos, buscando oportunidades para atacar a los suscriptores en todo el mundo. En el último mes, ha habido un fuerte aumento en la incidencia de IRSF, llamadas automáticas, estafas por SMS, fraude de ingeniería social, DDoS y ataques cibernéticos.

    Los operadores y los clientes han estado enormemente tensos durante las últimas semanas. Necesitamos estar a la altura de las circunstancias para proteger sus intereses. Según lo vemos desde Subex, se pueden seguir los siguientes pasos para enfrentar los desafíos relacionados con el fraude de las telecomunicaciones:

    • Conciencia del suscriptor: se debe lanzar un programa de concientización del suscriptor de inmediato para que los consumidores desconfíen de los diversos esquemas fraudulentos que surgen durante el período de pánico y miedo. Un caso puntual según lo informado por uno de los operadores asiáticos es que la semana pasada muchos suscriptores que habían instalado las aplicaciones de actualización en vivo COVID-19 en sus teléfonos recaudaron la friolera de $ 0.16 Mn porque no sabían que las aplicaciones también tomarían el estado del teléfono, incluida la función de lectura y escritura de SMS.
    • Priorizar el monitoreo de alertas de fraude: el trabajo remoto tendría sus desafíos. Los equipos de gestión de fraudes deben priorizar las alertas, especialmente las que tendrían un mayor impacto en los suscriptores y actuar en consecuencia y fijarlas en prioridad.
    • Acciones correctivas de causa raíz: la solución ideada para eliminar las causas de la actividad fraudulenta reducirá las probabilidades de su recurrencia. Por ejemplo, en la red, el rango de los números de destino de alto riesgo puede bloquearse por un corto período si se detecta un ataque de fraude IRSF.
    • Comunicación y colaboración: debemos estar conectados digitalmente a todas las partes interesadas para que actúen con dureza en actividades fraudulentas en la red. El SLA con las partes interesadas puede ser refinado y ajustado adecuadamente para una acción más rápida. Este es uno de los elementos clave cuando todo el equipo trabaja de forma remota para respaldar las operaciones diarias.
    • Actualizaciones periódicas sobre los patrones de fraude emergentes / recientes: visite con frecuencia los foros de fraude para estar al tanto de los patrones de fraude emergentes / recientes elaborados por los estafadores. Los delincuentes siempre están atentos a arruinar los procesos y sistemas para fines nefastos. Muchos operadores han informado un aumento en las llamadas automáticas, estafas por SMS y ciberataques durante este período.
    • Realización de la gestión del fraude como parte del Plan de continuidad del negocio (BCP): es muy importante incorporar la gestión del fraude como parte del BCP de manera importante y garantizar que tengamos la máxima cobertura durante este período.

    Según nuestros cálculos, los equipos de gestión de fraudes deberían estar más atentos y ágiles que nunca para enfrentar los nuevos desafíos del fraude de telecomunicaciones que se generalizaron durante este brote global de COVID-19. Los administradores de fraudes son superhéroes cuando se trata de generar confianza con los clientes.

    ¡Manténgase seguro y saludable!

    Para comprender cómo puede detectar y prevenir estafas y llamadas no deseadas utilizando modelos avanzados de aprendizaje automático

    Descargue el Estudio de Caso

  • Telecom fraud managers fight against fraudsters during COVID-19 crisis

    Telecom fraud managers fight against fraudsters during COVID-19 crisis

    There is now a global outbreak of COVID-19 with the resultant lock-down, panic, and fear across the globe. We have been keenly following the media to keep ourselves updated about the situation. While, very reassuringly, more than 95% of the workforces have started working from home with possible secure connectivity, fraudsters have also been equally active, looking for opportunities to attack the subscribers all over the world. In the past month, there has been a sharp increase in the incidence of IRSF, Robocalls, SMS Scams, Social Engineering fraud, DDoS and cyber-attacks.

    The operators and customers have been enormously strained during the past few weeks. We need to rise to the occasion to protect their interests. In my view, the following steps may be taken to deal with the telco fraud-related challenges:

    • Subscriber awareness: A subscriber awareness programme need to be launched immediately to make consumers wary of various fraudulent schemes that are floated during the time of panic and fear. A case in point as reported by one of the Asian operators is that last week many subscribers who had installed the COVID-19 live update apps on their phones coughed up a whopping $ 0.16 Mn because they were unaware that apps would also take over the status of the phone including SMS read and write function.
    • Prioritizing the fraud alerts monitoring: Remote working would have its challenges. The fraud management teams need to prioritize the alerts, especially which would have more impact on the subscribers and act on it and fix them on priority.
    • Root-cause corrective actions: Solution devised to eliminate the causes of fraudulent activity will stem the probabilities of its recurrence. For example, in the network, the range of the high-risk destination numbers may be blocked for a short period if an IRSF fraud attack is detected.
    • Communication and collaboration: We must be connected digitally to all the stakeholders so that they act tough on fraudulent activities on the network. SLA with stakeholders may be refined and suitably tweaked for faster action. This is one of the key elements when the whole team is working remotely to support daily operations.
    • Regular updates on emerging/latest fraud patterns: Frequently visiting the fraud forums to be abreast of the emerging/ latest fraud patterns worked out by the fraudsters. Criminals are always on the lookout to ruin the processes and systems for nefarious ends. Many operators have reported an increase in the robocalls, SMS scam & cyberattack during this period.
    • Making fraud management as part of the Business Continuity Plan (BCP): It is very important to incorporate fraud management as part of the BCP in a major way and ensure we have maximum coverage during this period.

    In my reckoning, the fraud management teams ought to be more vigilant and agile than ever before to meet the new challenges of telecom fraud becoming rife during this global outbreak of COVID-19. Fraud managers are superheroes when it comes to building trust with the customers.

    Stay safe and stay healthy!

    To understand how you can detect and prevent scam and spam calls using advanced machine learning models

    DOWNLOAD THE CASE STUDY

  • How big is the impact of the IRSF Fraud and 5 simple strategies to control IRSF

    How big is the impact of the IRSF Fraud and 5 simple strategies to control IRSF

    International Revenue Share Fraud (IRSF) is one of those fraud types that has been alive for two decades now, all because of the fraud being intricate in its pattern while the approach to it being still very reactive. Here, the motive of the fraudster is to receive the revenue share from the termination charge on international premium numbers. The fraudsters abuse the telecom operator’s infrastructure to artificially inflate traffic onto high-risk international destinations with the intention of non-payment. This fraud is common across geographies and has an estimated fraud loss of USD 5.04 Billion (The highest fraud loss contributor) as per the Communications Fraud Control Association (CFCA) Global Fraud Loss Survey, 2019.

    Lack of adequate steps taken to protect the network has caused this fraud to grow by leaps and bounds. In this fraud, the attacker usually tries to exploit the vulnerabilities of the Telecom Service Provider’s assets and attacks by either calling to unallocated number ranges or land calls onto international premium rated services or illegitimately route calls to short stopped mobiles. Subscription fraud, PBX hacking, Arbitrage Margin, SIM Cloning, Device theft and abuse of promotional services are often the commonly used methods for executing the fraudulent practices. The fraud is also quite common with many fixed line providers.

    In my experience of working with multiple operators, globally, I feel that the most common challenge faced by operators is in understanding the fraud pattern and method used by the attacker. The impact on the operator becomes brutal when fraudsters use unknown patterns of execution and sophisticated techniques to attack the network. IRSF attacks from roaming network, call conferencing, call forwarding, calling cards, negative margin abuse for products and services are among the more popular methods for a fraudster in launching attacks.

    Also, the lack of regulatory precedence in governing the way of carrying out business with international carriers is not sufficiently strict, setting the perfect breeding ground for fraudsters to flourish.

    Why has this fraud grown in leaps and bounds and how do I ensure control proactiveness?

    Traditional and reactive fraud countering mechanisms as of date do not have a full-proof solution, and one of the biggest reasons is that there are not enough fraud controlling strategies, mechanisms, and systems in place. IRSF, unlike other fraud types, requires a continual and proactive measure for control. More than just the “run-of-the-mill” detection techniques, the fraud type requires a well-planned control and mitigation steering strategy and here are six simple strategies, to begin with:

    • Fraudulent practices have become cleverer over time.

    If we brag of the fact that the fraud detection technologies have become quite sophisticated over time, we must not forget that the fraud practices too have gained an equal amount of intelligence. Fraudsters these days are quick to realize technology loopholes and system fault lines. It does not take much for fraudsters today to detect the fraud finding patterns and control logic of CSPs and identify the loophole in the system. In order to counter the fraudster’s attempt of IRSF, study of method and pattern become a critical process. Also use of SIP monitoring technique to identify devices/tool such as SIP vicious can help telcos to prevent IRSF. A mix of AI/ML techniques and models can be used to detect new IRSF fraud patterns with automation and build IRSF intelligence e.g.: trends in calling patterns.

    • Demoralize your IRSF attacker

    Letting your attacker attack you to dig his own grave sounds like an oxymoron? Actually not! It is, in fact, possible to have a honey-trap system in place where you lure the attacker to launch the attacks onto it without a fruitful outcome. The more the attacker’s attempts fail, the less hopeful they strive any further. Additionally, gathering intelligence from trusted suppliers who can provide information about prominent fraud groups and support surgical blocking of international number ranges has proved to be a successful strategy globally to counter IRSF.

    • Think of the customer and protect their interests

    IRSF not just drains away revenue resources but also can cause customer dissatisfaction, causing them to churn out of the network eventually. IRSF not only targets retail accounts but enterprise customer is a key risk group costing the telecom operator millions of dollars. Hence it is crucial that we don’t ignore whenever a customer complains of frequent cross-connections or call diversions for international calls.

    • Have an “Anytime-Anywhere” vigilance strategy with automation to your advantage

    The detection processes for IRSF may be complicated and resource-intensive at times. However, having the right strategies, the right processes with the right amount of automation applied to them can help the business in a significant way. I personally recommend a 24 x 7 detection strategy to be put in place to counter the IRSF attacks. From the cases that I have dealt with, it’s my observation that though IFRS attacks happen round the clock, however, the wee hours of the morning or off-business hours are critical target. Having a rotational manpower strategy can really work wonders at times. However, there could also be instances where having a 24*7 approach may not be possible owing to the lack of capital or high cost of human resources. In such instances, a mix of the automation of detection processes and human intensive operations during crucial hours will be of value.

    • Never ignore negative margins

    Negative margins can occur at any level. It could emerge while planning the pricing strategies of the products, services, use of calling cards in international destinations or interconnect agreements. Feeble margins on profits can often open a pandora’s box for fraudsters. Just the basic knowledge on negative margins is enough for fraudsters to break open mayhem. Trend reports on traffic patterns with priorities given to partnerships with frugal margins can save the day!

    • Pursue strategic knowledge partnerships to establish fraudster intelligence

    Sharing knowledge and having a supportive ecosystem for interaction with carrier partners and vendors in the value chain can be a practical step closer to proactiveness. Also, MoU’s established with industry forums and CoEs like GSMA, CFCA, RAG Blockchain for Wangiri, and others can help CSPs gain information such as PRS test numbers and services, high-risk range numbers, unallocated number series which can be used as vital sources of references to counter this fraud. Telecom operators can also build up the internal defense by establishing service controls e.g. restrictions on the use of international and roaming capabilities for certain customers. And restrict international call forwarding, multi-party calling, etc.

    When I say a reactive approach for AI / ML based IRSF fraud detection, I mean that much of the effort and systems built towards countering the fraud are in silos and so are the human efforts that go into it. By a proactive system, I mean a system that is quite unified in its approach and can perform end to end operations associated with the fraud type. A proactive Fraud Management system shall flag the first call in roaming, track significant deviation in usage behavior, high volumes of international traffic to high-risk destinations, sequential dialing, etc. and couple it with the use of knowledge databases like Subex IRSF data intelligence that includes unallocated number ranges, high-risk ranges, known fraudulent numbers to support network-based blocking and/or integration for early identification of high-risk behaviors and automated blocking, where required.

    One of the many ways of building a more proactive and unified system is to go the AI (Artificial Intelligence) way. A well thought out AI technology strategy can really help detect the fraud at a very early stage and help you choose the right controls for specific problems in question. It aims to reduce the time taken by the laborious human efforts that go into the detection stage while helping analysts and investigators concentrate on the need of the hour. Much as the famous English saying goes “Every cloud has a silver lining,” the impact of the IRSF can considerably be reduced by just broadening the organizational perspectives towards the fraud.

    Subex has recently partnered from Biaas for IRSF data Intelligence, To know how you can benefit from this partnership

    Download the flyer

  • Collaboration – The key to combat IRSF fraud

    Collaboration – The key to combat IRSF fraud

    Fraud continues to be a major problem for telecom operators, costing them billions of dollars annually. While telecom operators are continuously innovating to create new avenues of revenue streams to fight declining revenue margins from Voice and SMS services, technological advances are empowering fraudsters to evolve their fraudulent practices to tamper into the network. Telcos need to have access to the right threat intelligence information to combat fraud.

    International Revenue Share Fraud (IRSF) is one of the frauds which telcos have been trying to overcome for decades but still struggle to solve. Fraudsters usually exploit the vulnerabilities of the Communication Service Providers (CSPs) assets and attack by either calling to unallocated number ranges, landing calls onto international premium rated services, or illegitimately routing calls to short stopped mobiles. Subscription fraud, PBX hacking, Arbitrage Margin, SIM Cloning, Device theft, and abuse of promotional services are often the commonly used methods for executing fraudulent practices. IRSF attacks from the roaming network, call conferencing, call forwarding, calling cards, negative margin abuse for products and services are also some of the more popular methods for a fraudster in launching attacks. CSPs need to look to overcome the IRSF fraud menace to avoid revenue losses, network clogging, poor customer, and partner experience and negative impact on the brand image.

    While the Fraud Management (FM) system needs to be in place to overcome IRSF, one of the ways to tackle IRSF fraud is to have access to global number threat intelligence information. CSPs can configure their FM system to utilize this threat intelligence to detect and prevent fraud. To empower Subex ROC™ Fraud Management customers with threat intelligence information, Subex has recently partnered with RAG Wangiri blockchain consortium to provide its customers access to real-time threat intelligence to combat Wangiri fraud.

    As a next step, Subex is now partnering with Biaas, a leading expert in global number plan management for Pricing, Assurance, and Fraud Management within the telecommunication industry for IRSF threat intelligence. Through this partnership, Subex aims to provide its customers access to a powerful global number intelligence database that uses real-time information to battle International Revenue Sharing Fraud (IRSF). CSPs will have access to the following by subscribing to this database:

    • IRSF Test Number Database : Intelligence numbers gathered from IPRN websites and other sources. This will enable the CSP to identify if calls on their networks are being made to any IRSF Test Numbers as calls to IRSF Test Numbers are often an indicator that a fraud is about to happen.
    • Unallocated Destinations Database : Number ranges that are not allocated in any National Numbering Plan and should therefore see no legitimate traffic – any calls made to these destinations can confidently be flagged as fraudulent. This data even includes Unused Destinations, which appear allocated and valid but are not used by any operators currently. CSP will able to identify calls to expensive unallocated or Unused/Unassigned International destinations. CSP can use this data in many ways to pro-actively prevent or reduce such IRSF and other international voice frauds.
    • Allocated Destinations Database : Number ranges that are currently allocated to various operators. CSP will have access to tailored lists of International Higher Cost destinations (e.g. depending on geography or call types/tariffs) which can be utilized to assign higher priority to those potential frauds which would cause losses.
    • Digit String Length Database : Intelligence on the length of the numbers that are gathered from traffic analysis which can allow detection of fake calls made by fraudsters to destinations of invalid lengths.

    CSP will also have access to international fraud helpdesk run by expert Biaas professionals to facilitate fast and accurate issue resolution and decision making. By having access to this critical intelligence from Biaas, telecom fraud management teams will be able to effectively configure multiple types of defenses in the form of rules and real-time actions to keep fraudsters at bay. Combining this effective number intelligence with rich fraud detection capabilities provided by ROC Fraud management, CSPs will now have greater control in fighting IRSF fraud thereby directly protecting their revenue losses.

    To know more about how you will benefit from this partnership

    Download the flyer now!

  • What is Wangiri Fraud and how does it impact telecom operators?

    What is Wangiri Fraud and how does it impact telecom operators?

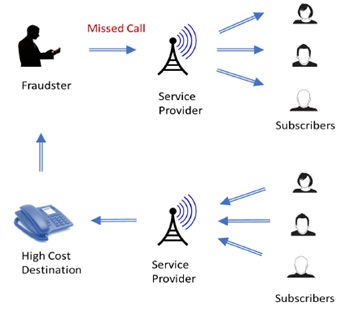
    Wangiri fraud, a callback scam dates has its origin to the Japanese word which means “one ring and cut”. Telecom operators are facing this for over a decade now and this is only growing exponentially year on year around the globe. In Wangiri, a fraudster gives a missed call to several victim’s phone numbers of different countries from an international or unusual number. To the user, the CLI (caller number ID) is modified in such a way that it looks like a genuine call and when the victim calls back, it turns out to be a premium rate service (PRS) number owned by fraudster for which the victim is charged heavily for the calls. The fraudster intends to keep the victim on hold to increase the billed amount. The premium rate service provider pays the fraudster a certain share of the call revenue for each minute of call received by the premium rate number.

    As per the CFCA 2019 fraud loss survey report, Wangiri is one of the top 5 fraud methods used by fraudsters to carry out fraudulent activities. It is also estimated that telcos are losing close to USD 1.82 billion globally to this fraud.

    FIGURE 1.1: Wangiri Fraud

    Impact of Wangiri fraud on telecom operators

    Telcos incur both direct and in-direct loss due to Wangiri Fraud. Wangiri impacts the customers adversely resulting in customer churn due to high customer dissatisfaction from bill shocks and bad customer experience. It also has a negative impact on the operator brand image as subscribers would complain about the high call rates charged to them without them being aware of it. There is also an impact on the cost due to the increase in customer management.

    Why Wangiri cannot be eliminated?

    The two main reasons due to which Wangiri cannot be eliminated but can be managed are:

    • There is no regulation defined on the carrier business causing the fraudster to take advantage of the vulnerabilities of the carrier network.
    • The lack of visibility on the end carrier who is terminating the call is another reason why Wangiri can’t be eliminated.

    The end carrier who terminates a fraudulent missed call is not aware of the fraudster details and the country from which call has originated is a high-risk destination or not. Better awareness at the carrier level can significantly decrease many Wangiri cases.

    As is clear from the statistics, Wangiri is eating a good chunk of the overall telecom revenues globally and needs to be addressed by the operator. Here is an interesting blog which talks about 8 simple strategies for telcos to combat Wangiri fraud. We conclude that Wangiri fraud cannot be eliminated, but its adverse impact of direct and indirect losses to the operator can be minimized to a large extent by having a robust fraud management system that can monitor the calls at source and tear down the calls in real-time.

    A tier-1 Middle East based telecom operator leveraged Subex’s Fraud Management’s signaling intelligence to detect and prevent Wangiri frauds.

    Read the case study now!

  • SIM SWAP FRAUD: Stepping into the fraudster’s shoes!

    SIM SWAP FRAUD: Stepping into the fraudster’s shoes!

    “Lose a credit card and the loss may be in thousands… Lose a SIM Card, the loss is irreparable”

    Last week, Twitter CEO Jack Dorsey became the latest high-profile account to be targeted by SIM swappers. Dorsey’s account sent several tweets, including some with racial slurs and others that defended Nazi Germany. Luckily for him, his account was secured soon after, and the consequences weren’t catastrophic. However, there have been many instances where SIM swappers have left victims in a really troubled state – especially the ones targeted for monetary gains.

    SIM swap is a type of phishing fraud that poses a serious threat to customer along with the telecom and the banking environments. The SIM SWAP fraudster in here obtains an individual’s banking details through vishing/smishing/phishing techniques or by purchasing these from organized crime networks. They then use this information, including personal details sourced via social media, to pose as the victim to the mobile network operator and fool them into cancelling and reactivating the victim’s mobile number to a SIM in their possession. As a result, all calls and texts to the victim’s number are routed to the fraudster’s phone, including one-time passwords for banking transactions. After receiving a one-time pin or password from a bank, the fraudster can then potentially access the customer’s bank account and transfer funds. The SIM SWAP fraud impacts not just the victim, financially but also the telecom operator and the bank, equally. As non-adherence to consumer interests and protection, in many countries, both the entities (the telco and the bank) are legally liable to compensate the victim for his/her financial losses. When the loss is in millions, the impact is very grave!

    Have you ever taken a moment to pause and think from a fraudster’s perspective to counter the fraud? Well most blogs that you will find on the internet on SIM SWAP will tell you ways (in bulletin points) as how to protect your assets from the SIM SWAP fraud. However, I am quite sure that there will only be a handful of blogs that will tell you how a SIM SWAP fraudster thinks in-order to be able to protect your customers from such attacks.

    Without much ado, let me take you through the 4 vicious stages involved in the SIM SWAP fraud attack which will help you understand your SIM SWAP fraudster better and stay ahead of them on any given day!

    Stage 1 – “Cherry picking and stalking”

    Fraudsters are always on the loom to pick on their fraudsters and the social media, has, in a great way helped them in getting away with their desired schemes. A SIM SWAP fraudster may look for a high-profile customer or a prosperous and wealthy business personnel who generally solicits with prospective clients over social media. The SIM SWAP fraudster here could impersonate one such client, send out a connection request and start to closely monitor the victim’s activities. The SIM SWAP fraudster can even hijack an account of the victim’s affiliate to initiate conversations/get more information about the victim. In events where the victim does not have enough digital footprints, SIM SWAP fraudsters have even taken the road of dumpster diving and shoulder surfing!

    Stage 2 – “Impersonating the victim”

    At this stage, the fraudster has got all the information he/she needed to pass through the authentication protocols required to get hold of the victim’s assets. Once he/she has managed to convince the bank and Telecom Operator of his/her false identity, he/she goes on to take-over the customer’s personal assets such as his/her sim card or his bank account.

    Stage 3 – “Swindling at once”

    Having gained total control over the victim’s assets, the SIM SWAP fraudster now tries to extract monetary benefits from the victim’s assets at a single go. Here the victim is totally cut-off from his/her mobile network even without knowing it. By the time the victim gets to know that there are transactions carried out on his/her account without their knowledge, the damage is done!

    Stage 4 – “Covering it up”

    After having caused enough damage to the victim, the SIM SWAP fraudster lets go of the victim’s assets and goes on to hunt for another victim. The SIM SWAP fraudster makes sure that he/she makes enough improvisations to his/her fraudulent schemes so as not to appear like a serial offender, thereby leaving the law keeping forces with very little clue of the fraudster’s whereabouts!

    SIM SWAP fraud, unlike many other telecom/bank frauds requires a joint effort from the customer, the bank and the telco. However, catching hold of the SIM SWAP fraudster doesn’t require the brains of Sherlock Holmes! Vigilance and a little proactiveness on how a fraudster might possibly behave can help catch them at a very early stage. To counter the ill-effects of the fraud, top Telecom Service providers like AT&T, T-Mobile, Verizon and other are harping on customer authentication through the 2-Factor method even during telephonic conversations.

    However, I personally believe that not much is being done to study transactional pattern anomalies to identify potential fraudsters in the network and its high time bank authorities joined hands with telcos in countering the fraud. E.g. the telcos can notify the banks of change in a customer’s IMEI/MAC address/addition or modification of accounts/transactional abnormalities and then the banks can monitor the customer’s transactions for that week, in priority! Masking methods can be used during exchange of information to protect consumer interests. Telcos and banks can be more proactive by creating a database for reference where any changes made to the consumer’s profiles can be stored and looked up for instances of abnormal transactions. As preventative measures, customers can be advised by both the telcos and the banks to take enough care while sharing very personal and integral information such as card details, social security number etc. on social media or the public internet.  The SIM Swap fraud is known to cause serious collateral damage and reputational loss, however, a little care taken at the right point in time can work wonders!

    To know more about how you can stay vigilant about SIM Swap fraud, view this video.

  • ¿Por qué la inteligencia artificial impulsó la Gestión de fraude?

    ¿Por qué la inteligencia artificial impulsó la Gestión de fraude?

    La Inteligencia Artificial (IA) no es nueva y ha existido durante décadas. Sin embargo, con el advenimiento del big data y la informática distribuida que está disponible hoy en día, es posible darse cuenta del verdadero potencial de la IA. Desde lo que comenzó como una historia interesante en películas de ciencia ficción hasta programas como Alpha-Go que ha estado venciendo a los humanos, la IA ha ido evolucionando. La Inteligencia Artificial también se ha ramificado en múltiples subcategorías, como aprendizaje automático o machine learning, aprendizaje profundo, aprendizaje de refuerzo, etc.
    FM-1

    FM-2
    Una estrategia eficaz de gestión de fraudes (FM) incluye 3 pilares importantes: detectar, investigar y proteger. Creemos que la Inteligencia Artificial puede influir positivamente en los 3 pilares de la gestión del fraude, desde reducir los falsos positivos hasta ayudar a extraer el análisis de causa de raíz y crear una mejor experiencia del cliente en protección.

    En esta publicación, me gustaría ver el pilar inicial de la estrategia de Gestión de Fraudes: “Detección” y ver la influencia de IA en este paso tan importante. Un enfoque tradicional para la detección de fraudes ha sido a través de motores de reglas que podrían ser:

    • Condiciones en caso contrario
    • Umbrales
    • Expresiones
    • Evaluación de patrones de datos
    Estas son ampliamente conocidas como soluciones deterministas donde un evento desencadena una acción. Los mayores pros y contras de este enfoque es que se necesita la intervención humana para alimentar la lógica.

    Por ejemplo: para una detección basada en el umbral, los humanos tienen que alimentar el motor de reglas para que el recuento de registros por encima de cierto umbral sea sospechoso.

    Los siguientes diagramas muestran cómo se ve esto

    rule-engine

    Después de mirar el diagrama anterior, surge una pregunta importante, si este valor de umbral es una línea recta o puede doblarse según el comportamiento de los datos. Ahora hay formas para que el motor de reglas se comporte como se menciona en el diagrama,

    variable-threshold

    por ejemplo, en lugar de tener una sola regla, tengamos varias reglas

    • Por categoría de cliente
    • Por destino
    • Por edad de los clientes

    Y multiplique eso con otras dimensiones en los datos que son

    • Número de teléfono
    • Número de la persona que llama
    • Número llamado
    • Código de país

    Y multiplique eso con otro conjunto de medidas por dimensiones

    • Cuenta
    • Duración
    • valor

    Y arroje mil millones de volúmenes adicionales a los conjuntos de datos

    Rápidamente los equipos de FM terminan con algo como esto
    AI Blog1
    Pero lo que querían o soñaban era esto
    AI Blog2

    Ahora no digo que los equipos de FM no estén lo suficientemente capacitados para volar, pero un equipo de fraude en un proveedor moderno de Servicios Digitales debería estar más enfocado en otros factores importantes.

    machine-learning
    Entonces, veamos cómo una clase muy evolucionada de Inteligencia Artificial conocida como Aprendizaje Automático (Machine Learning) observa esta declaración del problema. En lugar de que los humanos alimenten la información del dominio o los umbrales, los algoritmos de aprendizaje automático extraen datos de comportamientos fraudulentos históricos y crean modelos. Estos modelos se utilizan para evaluar conjuntos de datos de producción reales para evaluar si ciertas actividades son fraudulentas o no. Una ventaja es que estos modelos son muy buenos para ver los conjuntos de datos desde múltiples dimensiones y medidas al mismo tiempo y para determinar si el evento es fraude o no.

    Este enfoque ayuda a lograr múltiples KPIs de equipos de gestión de fraude allí al aumentar la eficiencia.

    • Mayor precisión – debido a que la inteligencia artificial puede aprender y adaptarse a los escenarios de negocios más rápido, la inteligencia artificial puede aumentar significativamente la relación positiva verdadera
    • Reducción del tiempo de detección – qué tan rápido se puede detectar un evento de fraude
    • Autoaprendizaje – cómo, durante un período, los escenarios empresariales cambiantes y la estacionalidad en los datos se pueden adoptar para la detección de fraude
    • Inteligencia contra el fraude– cómo se pueden aprender y clasificar los comportamientos del cliente o de cualquier otra entidad para una mejor detección del fraude
    • Proactividad – capacidad de extraer patrones desconocidos que no se vieron en los datos anteriormente
    FM-4

    La aplicación de Inteligencia Artificial tiene sus propios desafíos importantes y requiere un nuevo marco de pensamiento, sin embargo, al observar el Tsunami de Datos que ha afectado a los equipos de gestión de fraudes, parece que un enfoque profesional de IA solo ayudaría a los equipos de Gestión de Fraude a escalar aún más.

  • How Artificial Intelligence and Machine Learning is the key to combat Identity Fraud

    How Artificial Intelligence and Machine Learning is the key to combat Identity Fraud

    In an increasingly digitally connected world, identity fraud is a growing problem. According to the Communications Fraud Control Association’s (CFCA) annual fraud survey, identity fraud took the top spot as the number one fraud method present globally and at individual companies. Also featuring as the first among the top ten fraud methods, identity fraud in telecommunication during the subscription process (subscription fraud) resulted in costs of $2.03 billion.1

    Identity theft, where the use of fabricated identities at point of sale, enables the fraudulent use of telecom services and/or perpetuates subsequent fraudulent activities, can result in serious implications in the present age. With highly interconnected 4G and soon to be launched 5G networks enabling not just value-added services but also financial services like mobile payments and banking, it opens up access like never before.  Identity theft can work as an entry point for myriad types of fraud or even terrorism. With access to secondary authorizations (PIN code verification), subscription fraud can be used for any number of illegal activities.

    This has facilitated an urgent need for a proactive and dynamic response to fostering digital identity security.

    Securing against Identity Fraud

    The answer to fighting fraud lies in detecting data anomalies in real time. For example, to tackle telecom fraud, the Technology Research Institute (TRI) has stated that, real-time point-of-sale identity verification services are an invaluable aid to stopping fraudsters from exploiting identity theft.2 Historically, rules have always been in the system. But in the increasingly connected world, effective fraud coverage is only possible with a combination of rules and applied Artificial Intelligence (AI) and Machine Learning (ML) technologies.

    With AI and ML technologies, companies are able to detect data anomalies in real-time and make decisions based on information as it happens, empowering them to anticipate and take proactive action. For instance, AI/ML techniques can use facial recognition technology to identify high risk by making checks against blacklists. ML can augment traditional rule-based systems to develop and train algorithms to determine the characteristics of traffic and identify anomalies that could end up being fraud.

    Furthermore, the immense amounts of unsecured data flowing in from connected devices onto operator networks can be secured only with AI and ML. AI technologies are equipped with the capacity to scale up efforts and enable fraud detection at a massive scale by handling the management of millions of customer or network data points.

    As networks continue to expand and new fraud schemes continue to evolve, a combination of rules and applied AI/ML models will serve as the most effective way in combating identity fraud.

    If you are interested to learn how AI /ML techniques can help you combat Identity Fraud

    DOWNLOAD WEBINAR RECORDING NOW!

    1 . https://v2.itweb.co.za/whitepaper/Amdocs_LINKED_2017_CFCA_Global_Fraud_Loss_Survey.pdf

    2 . https://technology-research.com/products/fraudmgt/telecom_fraud_management_executive_summary.pdf?_sm_au_=iTHSrnwsn4HFwT3q

  • 8 Simple Strategies for Telcos to counter Wangiri Fraud

    8 Simple Strategies for Telcos to counter Wangiri Fraud

    Wangiri is not new rather; it is one of the most commonly occurring telecom fraud. In a recent case, a fraudster gave a missed call to several users of different countries. When the users viewed the missed call on their mobiles, they thought that it was a genuine missed call and called the number back. That is where they got tricked! The fraudulent numbers were unusually long and originated from an array of exotic countries. These were premium rated numbers so when the users called back, the fraudster’s intention to extract maximum payment out of them was successful.

    In such scenarios, it is not just the subscribers but their operators as well who bear the losses. There is both a direct and an indirect loss for the operator. As per the latest CFCA 2017 global fraud loss survey, Telcos have lost close of 1 Billion USD to Wangiri Fraud alone, which is quite a lot!

    In my point of view, Wangiri cannot be eliminated entirely for two main reasons- there is no proper regulation on the carrier business, and there is lack of visibility on the end carrier who is terminating the call. The end carrier who terminates a fraudulent missed call is not aware of the fraudster details and whether the country from which call has originated is a high-risk destination or not.

    So, let’s look at how can telcos protect revenue and provide great customer experience?

    • Subscriber Awareness

    A pro-active approach to minimize Wangiri fraud would be, making the consumers aware of the fraud scheme. If a number appears to be suspicious, a quick search of the number in several free apps available online, would tell the customer if the number is a part of any ongoing scams or not. Several Fraud Management tools are readily available in the market to detect and prevent Wangiri.

    • Customer Experience Management

    As the customer is the king of any business, and hence Telcos need to manage the customer complaints effectively, which will, in turn, reduce customer churns. All employees in the customer care department should be well informed about the Wangiri fraud and how the customer care executives should manage the complaints related to this fraud.

    • IVR (Interactive Voice Response) Facility

    IVR Facility is a pro-active approach that can be adopted by the operators. Whenever a subscriber calls back to a high-risk destination upon receiving a missed call, the operator should have an IVR voice informing him about his called destination. This IVR voice message would make the subscriber cautious to drop the call.

    • Removal of International Services as the default service for a Subscriber

    In India, Telecom Regulatory Authority of India (TRAI) has announced a new mechanism to effectively protect the common interest of mobile subscribers. TRAI has said that international service calling facility should not be activated on prepaid SIM cards without the explicit approval of the consumer. This measure is yet to be adopted by several other regulatory bodies globally.

    • Technology

    To protect customers from phone scams, T- mobile has introduced a new network technology. They have rolled out a scam ID by which customers are automatically alerted when an incoming call is likely a scam.

    Several other vendors are also coming out with similar technological solutions.

    • Routing Management of carrier:

    When a fraudster carries out the Wangiri fraud and gives missed calls to multiple subscribers, high amount of increased traffic can be observed on the carrier who routes these calls. If an operator monitors this activity, there will be a repetitive trend of increased traffic observed on the same carrier to route these calls. In such cases, an operator must take necessary precautions to route all the traffic through an alternative carrier. Routing the calls through a different carrier will help in breaking the chain between the fraudster and the linked carrier.

    • Control designing through FMS tool:

    Control designing through an FMS tool is required as it helps in early detection of Wangiri activity. An FMS tool assists in the discovery of Wangiri cases by monitoring the number of calls made by the fraudster. Artificial Intelligence & Machine Learning can play a significant role in detecting the Wangiri fraud.

    • Negative Margin Prevention

    In case of a negative margin occurrence, the number needs to be blocked by the operator immediately as it leads to direct impact in the revenue.

    I would conclude by saying the famous quote by Bill Gates, “Treatment without prevention is simply unsustainable”- though Wangiri fraud can never end completely, right preventive measures can minimize it significantly.

    If you are interested to learn how AI /ML techniques can help you combat Wangiri Fraud

    Contact Us

  • Account Takeover – Fraudster Intelligence

    Account Takeover – Fraudster Intelligence

    Account takeover fraud is one of the most common fraud types across the world. Fraudsters use the various methods to takeover an existing open account within the mobile operator or the banking instrument. The commonly used method of committing this type of fraud is vishing or smishing. As per CFCA fraud survey, account takeover accounted for an estimated fraud loss of 1.7 Billion US Dollars in the year 2017.

    In all these scenarios, the primary goals of the fraudster are to gain access to the account and (by-) pass the validation steps. In many situations, such validation may only require low-level knowledge-based authentication, so basic information obtained by the fraudster is used to validate and by-pass controls in place and to takeover the targeted account.

    I was investigating an Account takeover fraud case for one of the leading telecom operator in the APAC region wherein the fraudster used a different type of methods to commit this fraud. Many customers lost millions of dollars from their bank accounts without the knowledge after their account was taken over by the fraudster. On investigation, we identified that the fraudster’s primary motive was to takeover both mobile and banking account and then initiate multiple fraud transactions. He used Social Engineering, CLI spoofing, Spoofed website & Malware to commit the fraud.

    The Fraudster sequentially executed his schemes. He targeted only the high-profile subscribers in a region. He acquired all the information of the subscribers using social engineering methodology and called up the subscribers pretending to be a Bank executive and Mobile operator security officer. He asked the subscribers to download a malware-infested application from a spoofed website, following which he gained remote access to their mobile phones.

    The malware would read the SMS’s & call logs from the subscriber’s mobile and forward the details to fraudulent server. It also deleted the SMS & call logs from the mobile handset before the subscriber knew the same. The intention behind the reading of the SMS & Call log is to Bypass the second level authentication for completing the banking transactions. With this method in place, he was able the execute multiple transactions without the knowledge of the subscribers.

    Impact to Telcos?

    When subscribers approached law enforcement agency, the Law penalized both Telco and the bank and recovered from them, the amount lost by the subscriber. The Law took this action to protect the interest of the customers and secondly it was negligence from the service provider that led to the revenue losses of the subscribers.

    Telecom & banking service need to protect the subscribers from such fraud attacks by providing awareness to subscribers. Fraud management systems need have intelligence built into them to detect the fraud attack and control damages at an early stage.